Security team
Security team
The people keeping patient data secure, out of reach of attackers, and HIPAA compliant across everything Ultradoc does.
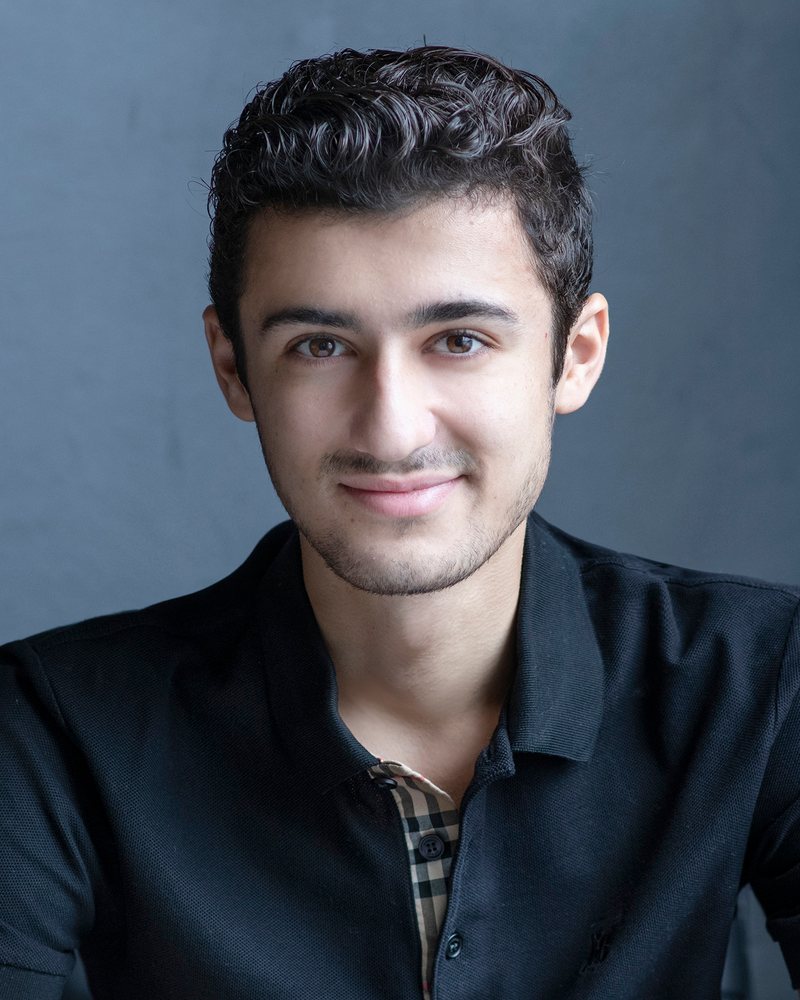
Vincent Sajkowski
Chief Technology Officer · Security Lead
Security contactsecurity@ultradoc.net
Security team
The people keeping patient data secure, out of reach of attackers, and HIPAA compliant across everything Ultradoc does.
Vincent Sajkowski
Chief Technology Officer · Security Lead
Vincent Sajkowski is Ultradoc's Chief Technology Officer and leads the company's security program. Vincent's focus is making sure patient data stays secure and out of reach of attackers.
That means maintaining HIPAA compliance across the entire Ultradoc suite: the patient app, faxes, patient notes, and every connection between Ultradoc and the systems it works with. No feature gets a lighter standard because it is small, new, or out of sight.
Security isn't switched on product by product. One set of safeguards runs underneath the entire platform, so every feature that touches patient data gets the same protection, and every feature we add inherits it.
All patient data Ultradoc stores is encrypted with AES-256, on infrastructure operated under signed Business Associate Agreements.
Every view, read, and edit of patient data is written to an append-only audit log of who, what, and when, kept for at least six years.
No outside provider touches patient data, AI included, without a signed Business Associate Agreement.
People see only what their role allows, and administrator access always requires multi-factor authentication.
And every integration, API, and connection in between.
If you believe you've found a vulnerability in Ultradoc, or suspect someone has accessed an account without authorization, email security@ultradoc.net. Reports are acknowledged within one business day.
The same protections run under every part of Ultradoc, from the chart to the patient's phone.
Tell us how your practice runs. We'll set Ultradoc up around it and connect it to the EHR you already use.